
An SSL certificate on a website, a code signature on software, a bank's payment system: the security of each one comes down to a single thing, the private key. If that key is stolen, an attacker can sign in your name, decrypt your traffic and impersonate you.
An HSM (hardware security module) is a dedicated device built to protect these keys. This guide explains what an HSM is, how it works, which types exist and when one is now mandatory.
What is an HSM?
An HSM is a security device that generates, stores and uses cryptographic keys inside tamper-resistant hardware. Its defining property is simple: the private key never leaves the device in plain text.
When an application needs to sign or decrypt something, it does not ask the HSM for the key. It sends the operation to the HSM, the HSM performs it internally and returns only the result. Even if the server is compromised, the attacker cannot reach the key itself.
Keys in software vs keys in an HSM
| Key in a file / in software | Key inside an HSM | |
|---|---|---|
| Where the key lives | On the server's disk or in memory | Inside tamper-resistant hardware |
| If the server is compromised | The key can be copied | The key cannot be copied, only used |
| Physical attacks | No protection | Keys are erased when tampering is detected |
| Audit trail | Depends on the application | Every key operation is logged on the device |
| Independent validation | Usually none | FIPS 140-3 / Common Criteria certification |
How does an HSM work?
An HSM's key lifecycle usually has four steps:
- Key generation: The key is created by the device's hardware random number generator. It never exists in plain text in a software environment.
- Access control: Roles define which application may use which key. Critical operations can require approval from several administrators (for example "2 of 3").
- Cryptographic operations: Applications connect through standard interfaces (PKCS#11, Microsoft CNG/KSP, Java JCE, OpenSSL) and have the HSM sign, encrypt or decrypt.
- Backup and high availability: Keys are backed up in encrypted form that only another HSM can open. Several devices can run as a cluster for uninterrupted service.
Related: How Entrust nShield HSM works
Types of HSM: network appliance, PCIe card, USB and cloud
HSMs do not come in a single form. The right choice depends on how many applications will use the HSM and where they run.
Network HSM appliance
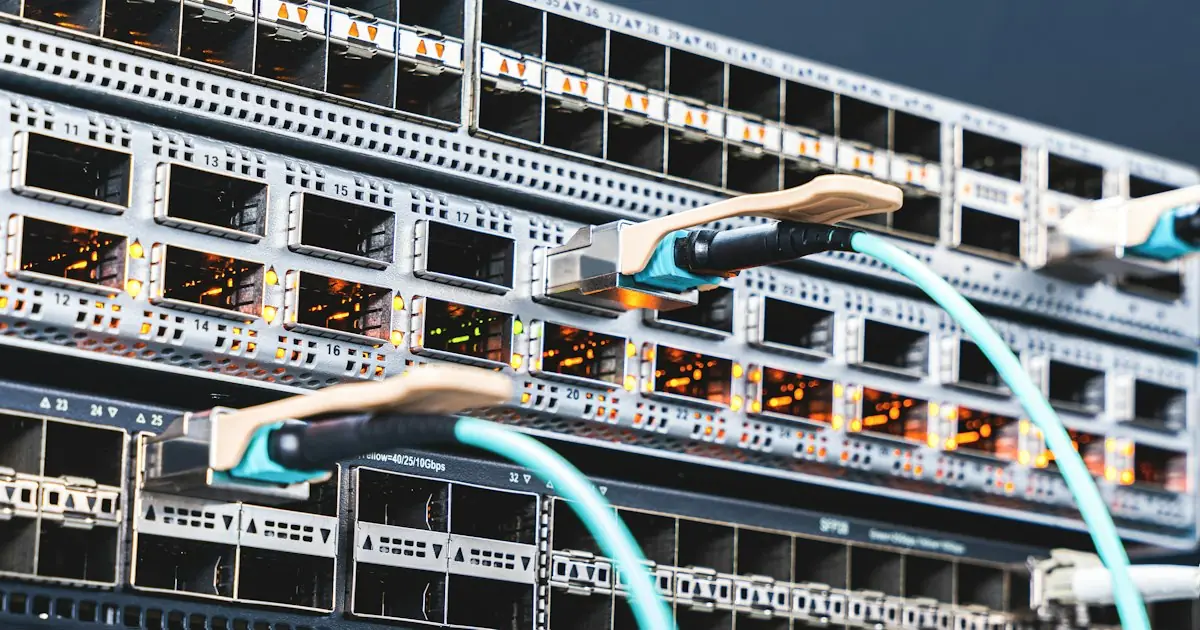
A rack-mounted appliance in the data centre that serves several applications over the network. It is the most common choice for PKI, certificate authorities (CA), database encryption and high-volume signing. Entrust nShield 5c and Thales Luna Network HSM belong to this group.
PCIe card HSM
A card installed inside a single server. Because it sits right next to the application, it offers low latency. It suits embedded systems and single-server workloads with heavy cryptography. Examples are Entrust nShield 5s and Thales Luna PCIe HSM.
USB HSM
A small, portable device. Its most common use is offline root CA keys: the device is connected only during a key ceremony and then stored in a safe. Thales Luna USB HSM is used for this purpose.
Cloud HSM (HSM as a Service)
Instead of buying hardware, you rent HSM capacity dedicated to you in the provider's data centre. Maintenance and hardware are the provider's responsibility. Entrust nShield as a Service is an example of this model; the large cloud providers also offer their own HSM services.
| Type | Best fit | Example |
|---|---|---|
| Network HSM | Many applications, PKI, high availability | nShield 5c, Luna Network |
| PCIe card | Single server, low latency | nShield 5s, Luna PCIe |
| USB | Offline root CA, key ceremonies | Luna USB |
| Cloud | Teams that do not want to manage hardware | nShield as a Service |
Related: Thales Luna HSM models
Where are HSMs used?
PKI and certificate authorities
If you run an internal certificate authority, the root and intermediate CA keys are the foundation of the whole chain of trust. Keeping these keys in an HSM is standard practice in PKI projects.
Code signing
If the key you sign your software with leaks, attackers can sign malware in your name. That is why, since 1 June 2023, the CA/Browser Forum requires the private keys of all code signing certificates to be generated and stored on hardware validated to at least FIPS 140-2 Level 2 or Common Criteria EAL 4+. For code signing, hardware is no longer optional.
For teams that sign rarely, the USB token supplied with the certificate may be enough. Teams that sign many builds automatically in a CI/CD pipeline usually choose a network HSM or a cloud-based signing service.
Related: Code signing certificates · Cloud code signing
Database encryption (TDE)
When transparent data encryption (TDE) is used in databases such as Oracle or Microsoft SQL Server, the master encryption key can be kept in an HSM. Even if the database files are stolen, they cannot be read without the key.
Key ownership in the cloud (BYOK / HYOK)
If you keep data in the cloud but want to stay in control of the encryption keys, you can generate the key in your own HSM and import it into the cloud (BYOK), or never hand it over and keep it on your side (HYOK).
Protecting TLS keys
High-traffic websites, banks and public institutions keep the private keys of their SSL/TLS certificates in an HSM so that a server breach does not leak the key.
Related: SSL certificates
What to look for when choosing an HSM
Answering these questions before you ask for a quote speeds up the process:
- Certification: What FIPS 140-3 (or 140-2) level and Common Criteria evaluation does the device have? Which level does your compliance requirement ask for?
- Form factor: Network appliance, PCIe card, USB or cloud service?
- Use case: PKI, code signing, TDE, BYOK, payment systems? Payment workloads (such as PIN processing) usually need a separate class of "payment HSM".
- Performance: How many signing or encryption operations per second do you need?
- High availability: A single device or a cluster? Do you need a second site for disaster recovery?
- Integration: Which interface do your applications use: PKCS#11, CNG/KSP, JCE or OpenSSL?
- Future readiness: Do you plan to move to post-quantum cryptography? Can the device support that move through a software update?
Sources: NIST CMVP list of validated cryptographic modules · CA/Browser Forum code signing baseline requirements
Entrust nShield or Thales Luna?
Both are widely used HSM families with FIPS Level 3 and Common Criteria evaluations. The choice usually depends on your existing infrastructure, the form factor you need and the integration ecosystem:
- Entrust nShield: key management with the Security World architecture; network appliance (5c), PCIe card (5s) and as a service (nShield as a Service).
- Thales Luna: one device split into independent partitions to serve different applications and teams; network, PCIe and USB options.
We can work out together which one fits your use case.
Related: Request an HSM quote
Frequently asked questions about HSMs
What is the difference between an HSM and a USB token?
A USB token is a small piece of hardware that stores a single user's key and is often supplied with code signing certificates. An HSM is an enterprise device that manages many keys and applications, offers high performance, can be clustered and keeps a detailed audit log.
What does FIPS 140-3 Level 3 mean?
FIPS 140-3 is the US NIST security standard for cryptographic modules. Level 3 requires physical tamper protection, erasure of keys when tampering is detected and identity-based access control. It replaces FIPS 140-2.
Is an HSM mandatory for code signing?
Hardware is mandatory, but that does not always mean an HSM appliance. Under CA/Browser Forum rules, code signing keys must be kept on hardware validated to at least FIPS 140-2 Level 2 or Common Criteria EAL 4+. That can be a USB token, an HSM or a cloud-based signing service.
Is a cloud HSM secure?
In a cloud HSM, keys are still held in FIPS-validated hardware; the difference is that the device sits in the provider's data centre. It suits teams that do not want to manage hardware and want to go live quickly. If you have data residency requirements, confirm the service region at the quote stage.
How much does an HSM cost?
The price depends on the model, performance tier, cluster size, licences and support term. That is why HSMs are sold on a per-project quote rather than at a fixed price.
Conclusion
An HSM separates your private keys from your servers and protects your most critical asset against physical and logical attacks. Hardware is now mandatory for code signing, and HSMs have become a common standard in PKI, database encryption and cloud key management.
DATASSL prepares quotes for Entrust nShield and Thales Luna HSM solutions based on your use case. Tell us briefly about your project and we will choose the right model and configuration together.
Related: Entrust nShield HSM quote · Thales Luna HSM quote
Yorumlar
No comments yet. Be the first to comment!
Write a Review